loader image
France Tax Agency Missed Data Theft Seven Weeks

In a breach lasting seven weeks, cyber attackers successfully siphoned off tax data from the France tax agency using stolen staff passwords. According to a report by France’s national cybersecurity agency, ANSSI, the perpetrators exfiltrated information on hundreds of thousands of taxpayers and businesses in June and July, without being detected. Investigators found that the […]
DIVD Breached by AI Agent in Messy Attack

The Dutch Institute for Vulnerability Disclosure (DIVD) was breached by an AI-driven cyberattack, which the organization described as ‘loud and very, very messy.’ The incident highlights a growing trend where attackers harness automated artificial intelligence to exploit cybersecurity organizations. The breach underscores the increasing sophistication of tools employed by cybercriminals, who take advantage of AI […]

WordPress Plugin Flaw Risks Takeover of 5M Sites

A critical flaw in the All-in-One WP Migration and Backup plugin threatens over 5 million WordPress sites, exploiting SQL injection risks. Known as CVE-2026-19949, the vulnerability affects versions up to 7.109, allowing attackers to take control of websites. Security researcher Jack Taylor, through Wordfence’s Bug Bounty Program, identified the issue, earning $5,761 for his discovery. […]

Malicious Apache Modules Hijack Brazil Sites

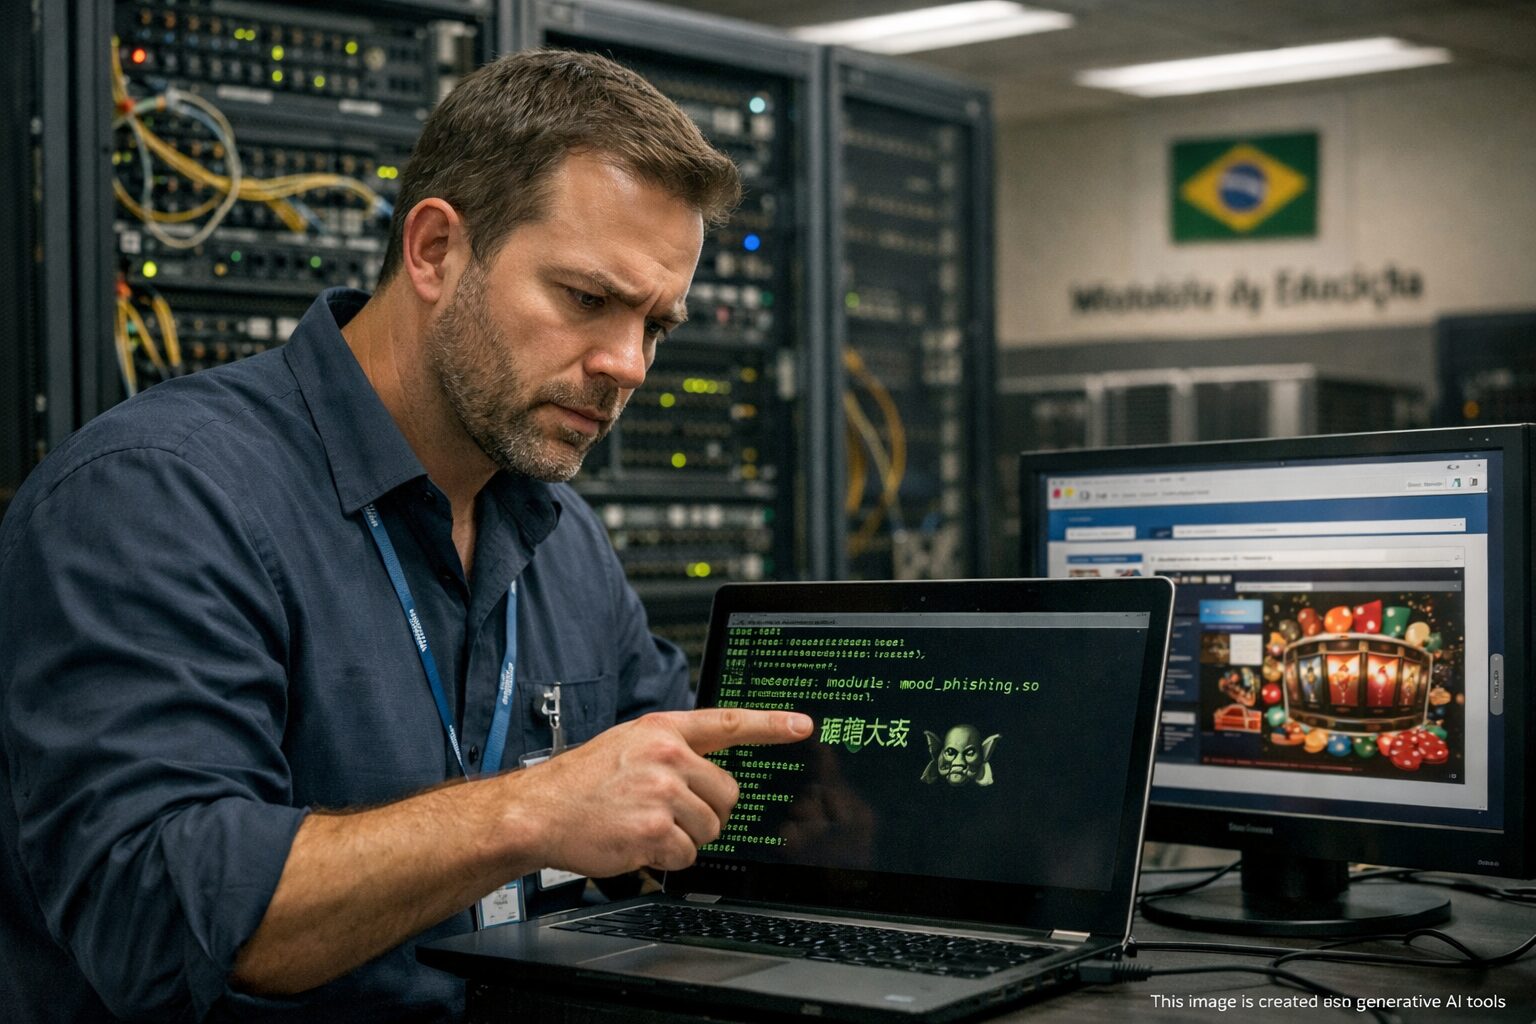
Brazilian government websites have been compromised with malicious Apache modules, turning them into unsuspected phishing proxies. This discovery indicates a shift from domestic cyber threats in Brazil to exploitation by foreign actors, with the Chinese-speaking Gambling Goblin group identified behind the attacks. These actors use compromised servers to disguise fraudulent content on legitimate domains effectively. […]

The Gentlemen Hackers Encrypt Networks in 24 Hours

The Gentlemen hackers, a notorious ransomware group, have accelerated their attack strategy to encrypt enterprise networks within 24 hours. By disabling endpoint detection and response (EDR) systems along with backups, these criminals swiftly render businesses vulnerable. As a ransomware-as-a-service operation, the group allows affiliates to target accessible organizations. Analysts from Sophos, who studied 15 incidents […]

Bank of Baroda Confirms Email Account Breach

The Bank of Baroda breach has raised concerns after the institution confirmed that an employee’s email account was compromised. This security lapse allowed hackers access to certain sensitive data, the bank reported. The bank assured stakeholders that they swiftly initiated measures to contain the breach and mitigate further risks. Security protocols were reviewed to prevent […]

Workers Ask AI First, Threatening Teamwork

A growing trend shows that workers ask AI first before turning to colleagues for assistance. A recent series of studies highlights a shift where 75% of employees prefer AI tools over human interaction for workplace queries. This inclination could potentially backfire, according to experts. They warn that relying heavily on AI could diminish interpersonal skills […]

Streamsoft BI Stores Passwords in Plaintext

Streamsoft BI stores passwords insecurely in its Business Intelligence software, exposing users to potential security threats. Researchers identified CVE-2026-50641, a vulnerability where the software retains passwords in plaintext. This flaw could provide attackers with unauthorized access, compromising sensitive information. Security experts urge businesses using Streamsoft BI to review their security protocols and consider applying necessary […]

UK Court Rejects Bahrain Immunity Claim

A UK court rejects Bahrain’s assertion of immunity in a high-profile spyware case that has riveted attention across the cybersecurity landscape. The court’s decision underscores significant allegations that officials in Bahrain orchestrated hacking operations. These operations allegedly enabled unauthorized access, data exfiltration from targeted computers, and interception of communications. Furthermore, the hacking purportedly allowed for […]

AnMed Health System Closes Offices After Malware

AnMed Health System closes several offices in South Carolina and Georgia after detecting a cybersecurity breach involving malware. On Sunday, the organization issued an online statement acknowledging the disruption and assuring efforts to restore its systems. The healthcare provider is actively working to determine the extent of the malware’s impact on its operations. Officials have […]

OpenSolution Quick.Cart Flaw Exposes Passwords

A recently discovered vulnerability in OpenSolution’s Quick.Cart software has raised cybersecurity concerns, as investigators identified a flaw storing passwords as plaintext, referencing CVE-2026-41874. This vulnerability poses significant risks to users, potentially allowing unauthorized access to sensitive information. Cybersecurity experts warn that plaintext password storage can lead to breaches, emphasizing the need for robust encryption methods. […]

AI Cyberattacks Hit 43% of Companies

As AI cyberattacks hit enterprises with increasing frequency, new research from CDW highlights a growing concern for companies worldwide. The study reveals that 43% of firms have already encountered AI-driven threats, particularly through phishing and malware-related strategies. This surge underscores the pressing need for organizations to bolster their defensive measures. Despite the rise in sophisticated […]